Home
You’re currently viewing our content for All Regions.
You can switch to a different region:
October 13, 2026
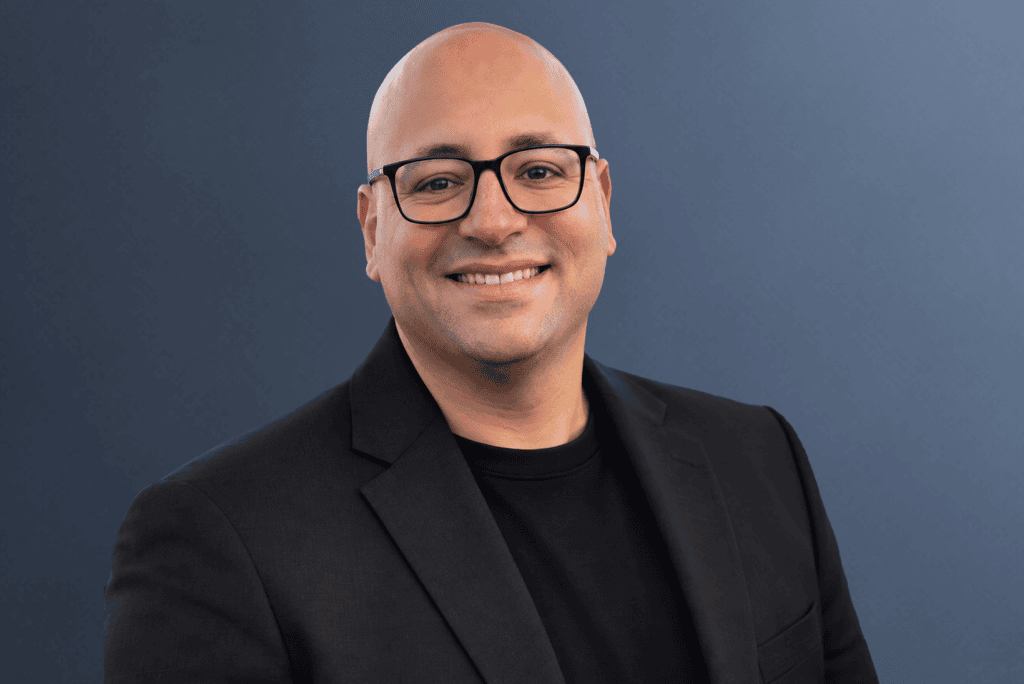
Amro Elmasry’s last meeting before this interview ended at 12:59pm.
It was a go-to-market session for a product that had already launched, the latest in a daily run stretching back more than two years.
“I’m a technical guy, so that’s what I do,” Elmasry shared.
“We’ve had a daily meeting on this product, so yes, I’ve been in more than 700 meetings. I don’t mind the constant check-ins. In fact, I’ve enjoyed them.”
As Founder and CEO of Extranet Systems – a Wollongong-based managed service provider (MSP) specialising in AI infrastructure, cyber security and cloud – Elmasry is a rare breed of entrepreneur.
Plenty of services firms have a product idea sitting in a drawer. A light bulb moment that captures the imagination but quickly evaporates – overshadowed by the darkness of day-to-day operations.
Elmasry’s view is that the drawer is where most of them die, and that the only way out is to give the idea the same standing as a paying client.
Hence why the meeting count of more than 700 is worth dwelling on. It is the method that matters.
“The key is to just commit, and not treat a new product like a side job,” Elmasry advised. “Even internally, we came up with 100 ideas. We actually started some of them, but we didn’t treat them as projects.”
The product is PentestOps, a continuous penetration testing platform built inside an MSP that already had software, infrastructure and security customers to look after.
The original idea came from a chore.
Extranet provides penetration testing as-a-service, and its engineers were losing days to the write-up. The alternative – common enough among MSP competitors – was to hand the customer 400 pages of scanned screenshots and label that as a ‘report’.
“Our guys use the tools but there’s lots of manual work,” Elmasry explained.
“Scanning and generating the report takes forever, because we actually want the content to be meaningful and helpful. So one day, we asked why we couldn’t just develop something to make our day-to-day operations a lot easier? We have our own dev team, our own infrastructure team, and we offer pen testing as one of our services. Why not?”
In other words, the capability was already in the building.
What was missing, however, was permission to develop it at scale. In response, Elmasry gave the idea a sponsor, a project management team and a commercial plan from the first week.
“We already had everything that we needed,” he recalled. “The only thing missing was the commitment of time. I was the internal sponsor, and we treated the project as if it were for a client.
“Our biggest risk was treating the idea as just another side task. It had to be a proper product we were going to commercialise. Guaranteed, without that structure we would never have launched. We’d have been distracted by the bigger projects coming in.”
From first conversation to real project took two to three months. From there to production took a little over two years.
Elmasry knew one part of the target market from the inside. When Extranet started in 2019, it was the kind of provider he is now selling PentestOps to.
“We were a small team,” he said.
“We didn’t have the budget or the capability to pay a couple of hundred thousand dollars for someone who knows what they’re doing. That’s why MSPs in that position are our first audience because they get the opportunities all the time.
“They just don’t have the resources, either because they can’t afford experienced cyber security talent or because it’s not their core business. The other products in the market are too expensive, or they’re glorified vulnerability scanners. That’s not what we wanted to do.”
The sizing exercise that followed turned a time-saver into Extranet’s flagship product offering.
“We saw huge commercial potential in the market, billions of dollars of it, and that’s why we committed because we didn’t want it to be just a nice-to-have option,” Elmasry said.
The first architecture decision was where the platform would live: a hyperscaler environment or Extranet’s own data centre.
“Funnily enough, we started with cloud,” Elmasry acknowledged. “The numbers made huge sense until the testing phase, and then we had to improvise.”
Compute was never the issue. Isolating each customer in its own environment on a managed cloud service was cheap. The trouble sat on the other side of the ledger.
“What killed us was the outgoing traffic,” Elmasry expanded.
“We factored for it, but we didn’t know how much. Egress was the killer, because this is a continuous validation platform. It’s not a pen-test that runs and stops.”
One fix was on the table: pass the bill through to the customer. Elmasry threw it out immediately.
“We can’t tell people, ‘our cost is X thousands of dollars just for traffic, so we’re charging you this, and good luck,’” Elmasry said. “Someone suggested we just deploy it and get customers to pay for the traffic. I said, ‘that’s a product killer.’”
So the platform came home.
“We were fortunate to have our own infrastructure team and our own data centre,” Elmasry added. “We just had to expand it, and quickly, because the traffic would have killed us.”
The expansion included NVIDIA DGX systems to run Extranet’s own model, which is trained on the company’s data and fed with live vulnerability intelligence. Each customer is connected to a private instance.
“It’s like someone else is doing the pen-test, only they’re very good at it and a lot quicker than any person,” Elmasry explained.
Timing also helped given that the big hardware orders went in before component prices ran riot.
“We ordered at the right time,” Elmasry accepted. “Memory is now four times what we paid for it. It was tempting because if we sold that memory today at half price, we’d still double our money.”
For sudden demand, Extranet now bursts into a partner cloud that carries no egress charge and is not a hyperscaler. Elmasry holds no grudge against the big platforms, however.
“We would have loved to use a hyperscaler but we had a choice,” Elmasry outlined. “Make it too expensive and maybe it takes off in 10 years, or give it a good price, not cheap but good, and it takes off now.”
Somewhere in the build, the product stopped being a pen-test.
“In the very early days, it was a pen-test,” Elmasry outlined.
“But once the project started, we said we don’t want to do a pen-test because there are plenty of those around. We want continuous protection, and that was the gap in the market.”
The shift came from a conversation he kept having with his own customers.
“The minute we finish the test, we go back and say, ‘OK, you have your test, you’ve ticked your compliance box. What now?’ And they say, ‘Well, we can do another test in six months.’ That was the reality,” Elmasry shared.
“We also read what some of those customers were handed by previous testers. It was just a scanner dump. I won’t mention names, but some of them were big, big names. And the customer just wanted to tick a box. Compliance done, move on.”
Elmasry’s objection is about time more than quality.
“A report is only as good as the date you finish scanning,” he highlighted.
“After that, it’s dated and you’re not protected anymore. I run my test today, find vulnerabilities and fix them. Then I do nothing for six months. What if a zero-day comes in, or someone’s already in the network doing something suspicious?”
PentestOps maps its findings to compliance frameworks as it goes, so an internal IT team can walk into an audit already knowing the result. Elmasry is also careful about where the product stops, and clear that an in-house security team does not remove the need for it.
“We’re not replacing an XDR or an EDR,” Elmasry qualified. “We’re filling the gap between protection, compliance and continuous compliance because I can be compliant by doing one test today, but I can’t be compliant all the time.
“If I write software, I don’t want to be the one testing it. I want someone else to. Whether my security team is junior, mid-level or expert, they can’t test their own work. I don’t want to tick a box and say I’ve done a pen-test. I want to be continuously vigilant about the threats out there, and to find and patch them before the bad actors do.”
PentestOps goes to market through two doors, and Elmasry is frank about which one he expects to carry the volume.
“Why sell to 10,000 people when you can sell to 200 MSPs and reach their 10,000 customers at the same time?” he asked. “They make their revenue without having to invest in resources. They win.”
The providers biting so far already manage security for clients but have no penetration testing practice of their own.
“They get leads and outsource them to a pen-testing company,” Elmasry observed. “Their margins end up tiny because they have to pay someone, and then who are we representing here? It doesn’t look good.
“We’re banking big on that MSP market, because the biggest gap is capability. They either don’t have it or it’s limited, so they get leads and turn them down. So what’s the call? Stand up a specialised cyber security department and pay big bucks, or get a platform that gives people who already do some security work a tool that handles the offensive side for them.”
The design concession to that channel is ownership. Providers get a super admin portal and Extranet stays out of sight.
“MSPs are fiercely protective of their clients,” Elmasry acknowledged. “They don’t want anyone to know who they are, and they get their backs up, which I understand. It’s fair. You spin up your tenants, you manage them, you white-label them, you do whatever you like.”
While firms that already run pen-testing teams were never the target, Elmasry now thinks a stretched practice could use the platform for capacity.
“If you’d asked me that when we were designing it, I’d have given you a different answer,” he noted. “Instead of one engineer managing five tests, one engineer can manage 50.”
The second door is direct to customer, and deliberately free of salespeople. Extranet put a blind question to its own staff: buy an unnamed product now at a fair price with no demo, or have someone talk you through it?
“Practically 100% self-service,” Elmasry said. “You want self-service but most services force you into a demo and through the sales process, and you lose a lot of potential customers that way, because they don’t want to hear another sales pitch.”
Plans are priced by the number of assets under test, an asset being an application, a server or a cloud service, and can be bought a month at a time.
“The sweet spot is the middle plan, for a medium-sized infrastructure where you’re scared that without it you’ll be in trouble on compliance,” Elmasry said. “You don’t buy the basic plan and get nothing. You get something good out of it, and that entices you to the next one.”
Demand has already turned up where nobody was looking. Extranet’s team went to a healthcare conference with a different pitch in mind and came back with a queue of medical professionals and health software providers worried about compliance.
“We went there for a specific target and got something else,” he said. “Another early customer just signed a contract with a major bank that required a pen-test every month.”
Despite early high demand in market, funding was its own test. The cost was engineers pulled off revenue work, then hardware nobody had budgeted for, some of which arrived roughly six months late.
“Our team was taken away from generating revenue,” Elmasry accepted. “But the main cost was hardware, because we didn’t factor it in until more than midway through the project. And it wasn’t just a few GPUs. It was the whole thing.”
Asked how he held his nerve as the number kept growing, Elmasry reached for a renovation as an example.
“It’s like building a house,” he explained.
“You’re almost there, you can see everything, and then the builder hits you with a massive bill. What do you do? This can be the difference between a multi-billion-dollar company and a few-million-dollar company. If you don’t take the risk, you live thinking, ‘I should have done it.’ And at the end of the day, it’s infrastructure. You can sell it, and you can sell the service.”
Encouragement came from unexpected directions. The project pushed Extranet most of the way to ISO 42001 certification for AI management, and award entries built on the product started landing. One regional awards night stays with him.
The larger return was internal, reaching staff in sales, infrastructure and Extranet’s overseas offices.
“Everyone was involved, from sales to infrastructure,” Elmasry said. “It built the team without us having to try. We all shared a common goal. Our goal with this product is to go global. We’re not just doing it here in Australia.”
The most developed route is one he did not plan. Extranet is in talks with internet service providers (ISPs) in the Middle East about selling continuous compliance as an add-on to an enterprise connection, for a fraction of the monthly bill.
“Honestly, that model came out of meetings,” Elmasry added.
“They sell enterprise internet connections in bundles, like mobile plans, so we’re working with them on a security bundle, a continuous compliance bundle. I don’t know if it would work here, but we’re considering it, because the market here is smaller than others.”
Entities in the US and Ireland are also in the works to meet local compliance requirements.
Elmasry would change almost nothing about the build. His one regret is the start date.
“One thing I definitely would have done is start this when I started Extranet,” he acknowledged. “If we’d begun the journey when we first got resources in 2020, we’d probably be significantly bigger than we are now.”
What got in the way was success.
“It’s very easy to land nice big wins and say, ‘OK, let’s just finish that,’ and you get stuck on one track,” Elmasry added.
“It’s very easy to let good ideas slip away. And we have let a few go, a private chatbot among them. When ChatGPT first came out, within a couple of months we had a product that did exactly the same thing. But it was niche. We were just selling it to individuals.”
A capable team makes the trap worse.
“Our team is good, and they’re confident in what they can do,” Elmasry said. “But if you don’t discipline that internally, it’s no longer a product, just a nicety. And we wanted a product.”
He also knows the engineer’s habit of building for an audience of one, so early versions went to clients for blunt feedback. Then the team shipped.
“We gave it to some clients and asked what they thought,” Elmasry continued.
“We made changes so it’s not what we see, it’s what people want to see. There’s no end. You could keep improving forever. You have to launch a good product and add to it, rather than chase perfection and never launch. You could have the best product and launch it two years late, and it’s pointless. Well, not pointless, but 10 times harder.
“That’s why our daily meetings for PentestOps continue. After launch, we’ve got to stay disciplined on the product. We don’t want to launch and stop.”
Inform your opinion with executive guidance, in-depth analysis and business commentary.